The short answer
A politically exposed person screening hit is a name match, not a finding. Resolving one means establishing whether the alert refers to your customer at all, what public function they hold and whether it is current, and what risk that role actually carries. PEP status is a reason for enhanced scrutiny, never in itself an allegation of wrongdoing.
What a politically exposed person is, and what it is not
The Financial Action Task Force defines a politically exposed person as an individual who is or has been entrusted with a prominent public function — heads of state and government, senior politicians, senior government, judicial or military officials, senior executives of state-owned corporations, and important political party officials — together with their family members and close associates. The category extends to foreign PEPs, domestic PEPs, and those holding prominent functions in international organisations.
The single most important thing to establish about the category is what it does not mean. Being a PEP is not a finding of wrongdoing, an allegation, or a reason in itself to decline a relationship. The rationale for the classification is positional: individuals in these roles have, by virtue of the role, the potential to abuse it for bribery, corruption or the movement of public funds. That potential justifies enhanced scrutiny. It does not establish anything about the individual.
This distinction is not academic, because it determines what the compliance function is actually being asked to do. It is not being asked to decide whether a customer is corrupt. It is being asked to understand who the customer is, where their wealth came from, and whether the relationship carries risk the institution has decided to accept — which is why source of wealth work sits so close to this, as set out in source of wealth and source of funds verification.
Why two vendors disagree about the same person
There is no official global PEP list. This surprises people, and it explains a great deal about why PEP screening behaves the way it does. Sanctions lists are published by governments — OFAC's SDN List is an authoritative instrument with legal effect. PEP databases are commercial products built by vendors from public sources, and each vendor makes its own editorial choices.
Those choices diverge on four axes. What counts as a prominent public function, and how far down the seniority ladder the definition reaches — a national minister is obvious; a municipal official or the deputy head of a regional agency is a vendor decision. How wide the family and close-associate net is cast, and how those relationships are evidenced. Whether and when a person is de-listed after leaving office, since FATF's guidance points away from automatic time limits and towards a risk-based assessment of continuing influence. And how thoroughly the underlying record is maintained.
The practical consequence is that a customer can be a PEP at one vendor, not at another, and a relative-of-a-PEP at a third. That is not a defect to be fixed by buying a better list; it is inherent to the product category. What it means for a programme is that the vendor's classification is an input to be assessed, not a verdict to be recorded — and that the institution's own written definition of who it treats as a PEP matters more than the label the tool applied.
A hit is a string match, not an identification
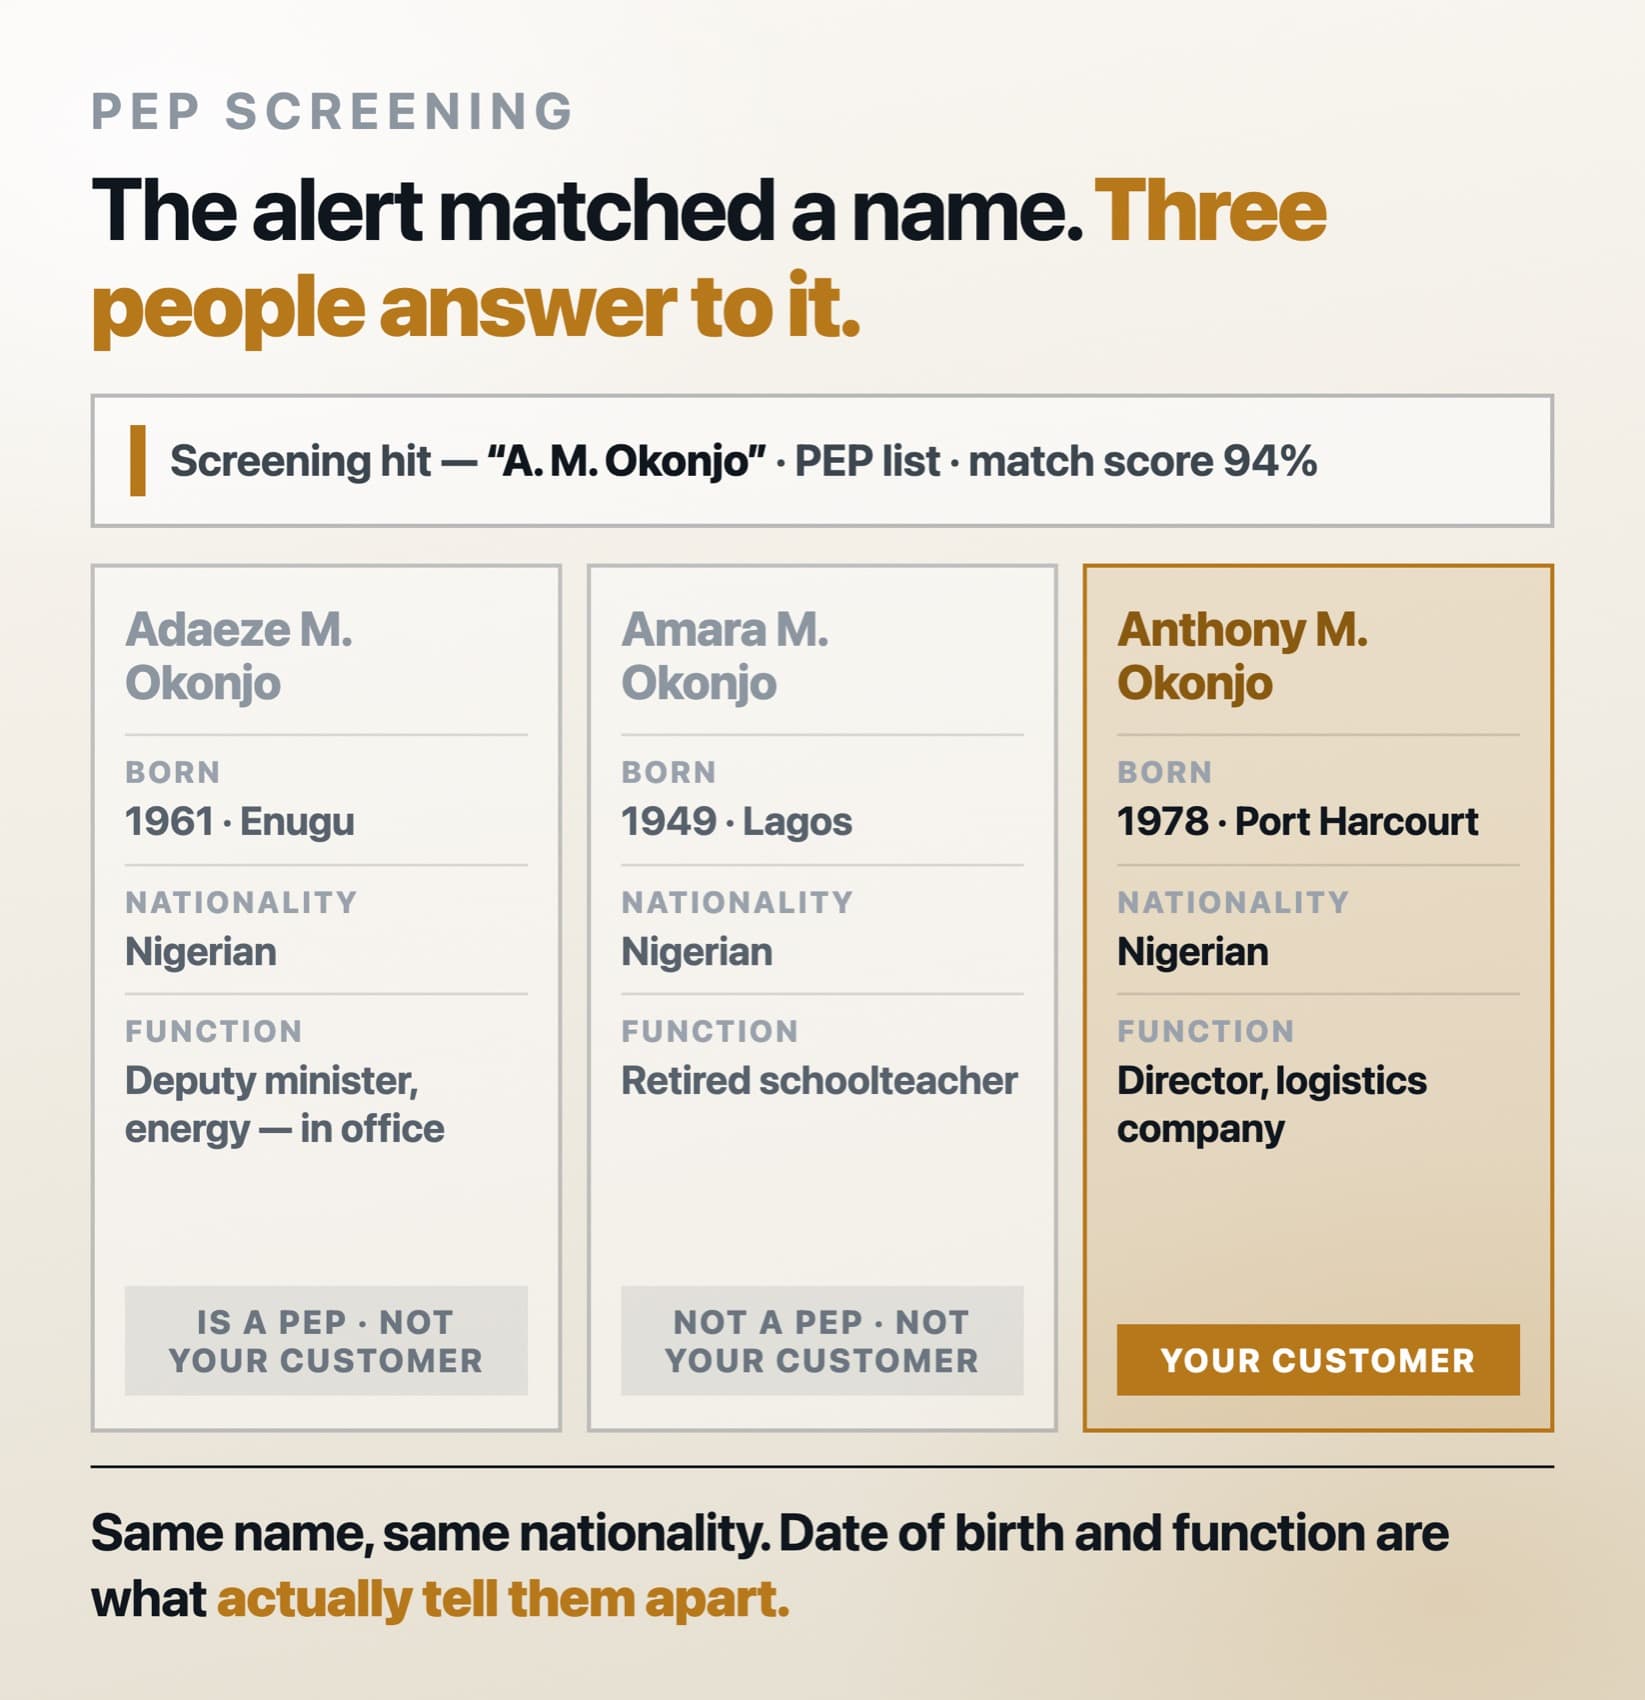
When an alert fires, what the system has established is that a name in your customer record resembles a name in a database, to some configurable degree of fuzziness. It has established nothing about whether they are the same human being.
Names are a poor identifier at global scale, and the reasons are systematic rather than occasional. Transliteration from Arabic, Cyrillic, Chinese and other non-Latin scripts produces multiple legitimate Latin spellings of the same name and identical spellings of different names. Naming conventions differ — patronymics, compound surnames in Hispanic and Portuguese-speaking countries, generational suffixes. Common names in populous countries produce very large numbers of genuine namesakes. And a screening system tuned to catch true matches will necessarily generate false ones, because the alternative tuning misses the person you were looking for.
So the alert is the beginning of the work. The question it poses is not "is this person a PEP" but "which person is this, and is that person a PEP" — and answering it requires discriminating attributes the screening system usually does not hold: date and place of birth, nationality and any second nationality, full name including middle and maternal names, and the individual's actual employment and address history.
The four steps that resolve a hit
A resolution that will survive an examination follows the same sequence every time, and each step produces a record rather than an impression.
- Discriminate the identity. Compare date of birth, place of birth, nationality, full name variants and known addresses between the customer record and the listed profile. The outcome is one of three: confirmed match, confirmed non-match with the discriminating attribute recorded, or unresolved — in which case say so rather than defaulting to either answer.
- Establish the function and whether it is current. Identify the specific office or role, the jurisdiction, and the dates held. A former junior official who left office fifteen years ago and a sitting minister for natural resources are both PEPs and are not remotely the same risk.
- Risk-rate the role rather than the label. What does the position actually control — public procurement, licensing, natural resource concessions, state enterprise contracts? What is the corruption risk of the jurisdiction? Is there adverse media, and if so does it survive attribution to this individual? Is the relationship direct, or is the customer a family member or close associate, and how close?
- Where the relationship proceeds, establish source of wealth and source of funds. This is where the enhanced scrutiny actually happens: not in flagging the person, but in independently establishing that their wealth has an explicable and lawful origin consistent with their known career — an evidential exercise rather than an acceptance of the customer's own account.
The two ways programmes get this wrong
Examiners find the same two failures repeatedly, and they sit at opposite ends of the same axis.
The first is under-resolution. Alerts accumulate faster than analysts can work them, and the queue is cleared by closing hits as reviewed with no record of what was reviewed or what was concluded. This is the more common failure and the more dangerous, because the institution has generated a documented alert and then documented nothing in response to it — which reads far worse on examination than never having screened at all. A programme in this state has bought the appearance of a control.
The second is over-blocking. Faced with alert volume and uncertainty, an institution declines or exits entire categories — all PEPs, all customers from a jurisdiction, all correspondent relationships in a region. FATF has been explicit that wholesale de-risking of this kind is not the application of the risk-based approach but a retreat from it, and that it pushes activity toward less transparent channels. In August 2020 the federal banking agencies and FinCEN issued a joint statement making a related point for US institutions: the Bank Secrecy Act regulations do not define "politically exposed person" and do not impose a categorical enhanced-review obligation on every such customer. The obligation is risk-based, which means a programme that automatically declines every PEP is not being conservative — it is substituting a rule for the assessment it was supposed to make.
An ongoing control, not a transaction check
This is where PEP screening differs most sharply from the deal-scoped sanctions and reputational work described in the sanctions and reputational due diligence M&A playbook. That exercise answers a question at a point in time, before a specific commitment, and then it is finished. PEP status does not hold still.
People become PEPs after onboarding. A customer is elected, appointed, promoted into a senior state-enterprise role, or marries into a family that already holds one. A customer's close associate takes office. Equally, people cease to hold prominent functions, and the risk associated with them decays — though FATF's guidance points to assessing continuing influence rather than applying an automatic expiry.
So the control has three components rather than one: screening at onboarding, periodic re-screening of the existing population at a frequency set by risk tier, and event-driven review triggered by changes the institution learns about independently — a change of employer, a change of address to a jurisdiction of concern, a significant unexplained change in transaction pattern, or adverse media naming the customer. The same architectural logic applies here as in third-party risk management: the platform runs across the whole population continuously, and the investigative layer resolves the small number of cases where the answer actually matters.
What the guidance actually requires
FATF Recommendation 12 sets the international standard. For foreign PEPs, financial institutions should have risk-management systems to determine whether a customer or beneficial owner is a PEP, obtain senior management approval for establishing or continuing the relationship, take reasonable measures to establish source of wealth and source of funds, and conduct enhanced ongoing monitoring. For domestic PEPs and those holding prominent functions in international organisations, the requirement is to take reasonable measures to determine status and then apply those enhanced measures where the relationship is higher risk.
In the United States the framing is different in an important way. The FFIEC BSA/AML Examination Manual addresses senior foreign political figures within a risk-based customer due diligence framework, and FinCEN's customer due diligence rule requires identification and verification of beneficial owners at twenty-five per cent equity plus a control person — but as the 2020 joint statement made explicit, there is no separate categorical PEP regime in the regulations. The obligation is to know your customer well enough to assess and manage the risk, which for a genuinely high-risk PEP relationship will look very much like the FATF measures, and for a low-risk domestic one may not.
The Wolfsberg Group's guidance on PEPs, produced by the major international banks, is the most useful practical statement of how the assessment is actually performed. It is worth reading alongside the regulatory material precisely because it is written by practitioners describing what a defensible file looks like rather than what a rule requires.
What a defensible resolution file contains
The test is simple and worth applying to a sample of closed alerts: could someone who was not involved reconstruct the decision from the record alone, two years later, without speaking to the analyst who made it?
That file contains the alert as it fired, with the vendor, the list and the match score. It contains the discriminating attributes compared and the conclusion drawn — matched, not matched with the reason, or unresolved. Where matched, it records the specific office or role, the jurisdiction, the dates held and the source establishing them. It records the risk assessment of the role, the jurisdiction and any adverse media, with attribution of that media to the individual rather than to the name. Where the relationship proceeded, it records the source of wealth and source of funds evidence, the senior approval obtained and by whom, and the review date and trigger conditions set.
Almost none of that is generated by the screening system, which is the point of this article. The tool identifies candidates for attention; the analysis, the attribution and the written conclusion are investigative work, and they are what an examiner, a correspondent bank or a court is actually reading. The wider discipline this belongs to is set out in what investigative due diligence is, and the integrity-focused version of the same method in the reputational due diligence playbook.
Key takeaways
- PEP status is positional, not accusatory: it identifies a role with potential for abuse, and it is a reason for enhanced scrutiny rather than a finding about the individual.
- There is no official global PEP list. Commercial databases apply their own seniority thresholds, family and associate definitions and de-listing practices, so a customer can legitimately be a PEP at one vendor and not another.
- An alert is a string match against a name, not an identification — transliteration, naming conventions and common names guarantee false positives in any system tuned to catch true ones.
- The two failure modes are under-resolution (closing alerts as reviewed with no record, which reads worse on examination than not screening) and wholesale de-risking, which FATF treats as a retreat from the risk-based approach rather than an application of it.
- In the US the BSA regulations do not define "politically exposed person" or impose a categorical enhanced-review duty — the 2020 joint statement made that explicit, and the obligation remains risk-based.
Frequently asked
10 questionsWhat is a politically exposed person?
Under the FATF definition, an individual who is or has been entrusted with a prominent public function — heads of state or government, senior politicians, senior government, judicial or military officials, senior executives of state-owned corporations, and important political party officials — together with their family members and close associates. The category covers foreign PEPs, domestic PEPs, and persons holding prominent functions in international organisations.
Does a PEP hit mean the customer has done something wrong?
No. The classification is positional rather than accusatory: it identifies a role that carries potential for abuse, and therefore justifies enhanced scrutiny. It establishes nothing about the individual's conduct. Treating a PEP designation as an adverse finding is one of the most common analytical errors in this area and leads directly to the over-blocking failure mode.
Why do different PEP databases disagree?
Because there is no official global PEP list. Unlike sanctions lists, which governments publish with legal effect, PEP databases are commercial products compiled from public sources. Vendors differ on how far down the seniority ladder a prominent public function reaches, how widely they cast the family and close-associate net, whether and when they de-list someone who has left office, and how well the underlying records are maintained.
How do you resolve a PEP screening alert?
In four steps, each producing a record. Discriminate the identity by comparing date and place of birth, nationality, full name variants and addresses, concluding matched, not matched with the reason, or unresolved. Establish the specific office, jurisdiction and dates held. Risk-rate the role rather than the label — what it controls, the jurisdiction's corruption risk, and whether adverse media attributes to this individual. And where the relationship proceeds, independently establish source of wealth and source of funds.
Why are there so many false positives in PEP screening?
Because names are a weak identifier at global scale. Transliteration from non-Latin scripts produces multiple valid Latin spellings of one name and identical spellings of different names; naming conventions vary with patronymics, compound surnames and generational suffixes; and common names in populous countries generate large numbers of genuine namesakes. Any system tuned loosely enough to catch true matches will generate false ones — that is the trade-off, not a defect.
Should a bank automatically decline PEPs?
No, and doing so is itself a compliance weakness. FATF has been explicit that wholesale de-risking of categories or jurisdictions is a retreat from the risk-based approach rather than an application of it, and pushes activity into less transparent channels. In August 2020 the federal banking agencies and FinCEN clarified that the BSA regulations neither define "politically exposed person" nor impose an automatic enhanced-review obligation on every such customer.
How is PEP screening different from sanctions screening?
Sanctions lists are government instruments with direct legal effect: a match, once confirmed, prohibits dealing and requires blocking or rejection. PEP status carries no prohibition at all. It is a risk indicator that triggers enhanced due diligence and, for foreign PEPs under FATF Recommendation 12, senior management approval, source of wealth enquiry and enhanced ongoing monitoring. Confusing the two produces either unlawful dealing or unnecessary exits.
How often should an existing customer base be re-screened?
At a frequency set by risk tier, and supplemented by event-driven review. People become PEPs after onboarding — by election, appointment, promotion into a senior state-enterprise role, or marriage — and close associates take office independently of your customer. Events worth treating as triggers include a change of employer, a change of address to a jurisdiction of concern, a material unexplained change in transaction pattern, and adverse media naming the customer.
When does someone stop being a PEP?
There is no universal expiry. FATF's guidance points away from automatic time limits and towards assessing whether the individual retains influence — through networks, continued informal authority, or a family position — after leaving office. A former minister who still directs appointments in a sector is a different proposition from a former junior official who left public life fifteen years ago, and a programme that applies a single fixed period to both is not performing an assessment.
What should a closed PEP alert file contain?
Enough for someone uninvolved to reconstruct the decision two years later without speaking to the analyst. That means the alert as it fired with vendor, list and match score; the discriminating attributes compared and the conclusion reached; where matched, the office, jurisdiction, dates held and the source establishing them; the risk assessment of role, jurisdiction and adverse media attributed to the individual; and where the relationship proceeded, the source of wealth evidence, the senior approval and who gave it, and the review date and trigger conditions.
Sources & further reading
- 01FATF Recommendation 12 and the FATF Guidance on Politically Exposed Persons (Recommendations 12 and 22)Sets the international standard: risk-management systems to determine PEP status, senior management approval, reasonable measures to establish source of wealth and funds, and enhanced ongoing monitoring for foreign PEPs, with a risk-based application to domestic PEPs and international organisation officials.
- 02FATF — guidance on de-risking and the risk-based approachStates that wholesale termination or avoidance of entire categories of customer, rather than case-by-case risk management, is not consistent with the risk-based approach and drives activity toward less transparent channels.
- 03Joint Statement on Bank Secrecy Act Due Diligence Requirements for Customers Who May Be Considered Politically Exposed Persons (Federal Reserve, FDIC, NCUA, OCC and FinCEN, August 2020)Clarifies that the BSA regulations do not define "politically exposed person" and do not require automatic enhanced due diligence for every such customer — the obligation is risk-based, which is the answer to programmes that categorically decline PEPs.
- 04FFIEC Bank Secrecy Act / Anti-Money Laundering Examination ManualAddresses senior foreign political figures within a risk-based customer due diligence framework, and is the document against which a US institution's handling of these relationships is actually examined.
- 05FinCEN — Customer Due Diligence Requirements for Financial Institutions, 31 CFR 1010.230Requires identification and verification of beneficial owners at a 25% equity prong plus a control prong — the mechanism by which a PEP holding an interest through an entity becomes visible at all.
- 06The Wolfsberg Group — Guidance on Politically Exposed PersonsWritten by practitioners at major international banks, it is the most useful practical account of how PEP status is assessed and documented, and of what a defensible resolution file contains as distinct from what a rule requires.